
Highlights
Annual training measures completion, while continuous risk measurement reveals actual exposure.
Attackers now exploit SMS, voice, and AI agents, not just phishing emails.
Independent verification can stop high-risk requests before urgency turns into an incident.
7 Best Ways to Prevent Social Engineering (2026)
Most organizations still measure social engineering readiness by asking one question: did the person finish the training? That's the wrong question. The better one is: how likely is this person to be attacked right now, across every channel available to an attacker, and what should we do about it?
That shift matters because the attacks themselves have changed. Social engineering used to mean phishing email. Now it means a spoofed voice call from "IT," a text message that looks like it's from a delivery service, or a video call with a face that isn't real. Social engineering vs. phishing is a useful distinction here: phishing is one channel inside a much bigger category that also includes vishing, smishing, and deepfake-driven impersonation.
The FBI's Internet Crime Complaint Center logged more than $16 billion in reported losses in 2024, a 33% jump from the year before, and phishing and spoofing were the single most-reported crime type by complaint volume that year. The attacks aren't slowing down. What's changed is how organizations need to respond.
What is Social Engineering?
Social engineering is any attempt to manipulate a person, rather than a system, into handing over information, credentials, or access. It doesn't rely on exploiting software. It relies on exploiting instinct: the urge to help, to respond quickly to authority, to trust a familiar name.
That's what makes it hard to stop with technology alone. A firewall can't tell the difference between a legitimate request from your CFO and a convincing fake one. The person on the other end has to.
Social engineering shows up across several channels, and most organizations only defend one of them:
Phishing: deceptive email designed to steal credentials or deliver malware
Smishing: the same tactic delivered by SMS or text message
Vishing: a phone call impersonating IT, a vendor, or an executive
Pretexting: a fabricated scenario, like a fake audit or helpdesk request, used to extract information
Deepfake impersonation: AI-generated audio or video used to impersonate a real person in real time
Phishing is the one most people picture first, but it's a single channel inside a much larger category. Treating social engineering as "the phishing problem" is exactly why so many programs miss the SMS, voice, and deepfake attacks happening around it.
Real-World Examples
Social engineering isn't a hypothetical. These three publicly documented incidents show how it plays out across different channels, and how much damage a single successful attempt can do.
MGM Resorts, 2023 (vishing)
Attackers linked to the group Scattered Spider called MGM's IT help desk, impersonated an employee they'd identified on LinkedIn, and talked their way into a password and MFA reset, no malware, no exploit, just a phone call. That single call led to a shutdown of slot machines, hotel key systems, and booking platforms across MGM's properties for several days. (Vox)
The Department of Justice has since brought multiple prosecutions against alleged Scattered Spider members, describing a pattern of social engineering, computer intrusion, and extortion across more than a hundred victim organizations. (U.S. Department of Justice)
Arup, 2024 (deepfake)
A finance employee at the Hong Kong office of the UK engineering firm Arup joined a video call with people who looked and sounded exactly like the company's CFO and several colleagues. Every participant except the employee was an AI-generated deepfake. He made 15 transfers totaling roughly $25 million before the fraud was discovered.
Arup's global CIO later confirmed the incident publicly, describing it as social engineering enhanced by technology rather than a conventional cyberattack. (CNN Business)
Operation reWired, 2019 (email/BEC, at scale)
This wasn't a single incident but a coordinated DOJ and FBI takedown of business email compromise schemes operating internationally. The operation resulted in 281 arrests across multiple countries and the recovery or disruption of roughly $118 million in fraudulent wire transfers, all built on the same pattern: impersonate a trusted executive or partner by email, and ask someone with access to money to move it. (FBI.gov)
Three different channels. Three different levels of technical sophistication. The same underlying weakness in all of them: a person trusted a request that felt legitimate in the moment, and nothing in the process forced a second check.
How to Prevent Social Engineering in 7 Effective Ways
Here are seven ways to actually prevent social engineering, not just check a compliance box.
1. Replace annual training with continuous, behavior-based risk measurement
The old way: run a mandatory training module once a year, log a completion rate, move on. The problem is that a completion rate tells you who clicked "next" on a video. It tells you nothing about who's actually exposed right now.
The Cimento way: measure human risk continuously. Behavior-based signals, how someone responds to a suspicious message, whether they've been targeted before, what systems they touch, build a real-time picture of exposure instead of a once-a-year snapshot. This is the core idea behind Human Risk Management (HRM): it treats risk as something that changes week to week, not something you measure with an annual quiz.
What this looks like: short, frequent nudges tied to actual behavior, not a long refresher nobody remembers by the following quarter. A person who's been targeted three times this month needs different attention than one who hasn't been targeted at all.
2. Simulate every channel attackers actually use, not just email
Training tells people what to look for. Simulation tells you whether it worked, and increasingly, email-only simulation misses most of the picture. Attackers have moved to SMS, voice calls, and AI-generated video and audio because those channels feel more personal and are harder to verify on the fly.
What this looks like: running phishing, smishing, vishing, and deepfake simulations against your own organization on a recurring basis, not as a one-off exercise. If you're only testing email, you're only measuring a fraction of your actual exposure. A person who spots a spoofed email might still hand over a password to a voice call that sounds exactly like their manager.
3. Put a verification step around every high-risk request
No amount of training stops a request that feels legitimate in the moment. An attacker impersonating a finance lead asking for an urgent wire transfer isn't targeting your network, they're targeting one person's judgment under pressure. If the only safeguard is that person's instinct in real time, it will eventually fail.
What this looks like: a callback protocol for anything involving money movement, credential resets, or access changes. Confirm the request through a separate, already-known channel, not by replying to the same email or calling the number the request came from. This single rule closes most business email compromise and vishing scenarios almost entirely, and it costs nothing to implement.
4. Harden the technical layer that sits underneath your people
Behavior change matters most, but it works alongside, not instead of, the basics: multi-factor authentication on every system that matters, email authentication (SPF, DKIM, DMARC) configured correctly, and spam filtering that's actually tuned rather than switched on and forgotten.
What this looks like: MFA everywhere it counts, paired with access limits so a compromised account can't reach more than it needs to. None of this stops a determined social engineer on its own, but it raises the cost of every attempt and buys time for the human-layer defenses to catch what gets through.
5. Measure real behavior, not just who finished the course
Here's where most programs quietly fail: they track completion, not outcomes. A 100% completion rate on a training module says nothing about whether risk actually went down. What matters is whether the people most likely to be targeted, executives, finance, anyone with access to sensitive systems, are getting measurably harder to fool over time.
What this looks like: a person-level risk score built from actual behavior across simulations and real incidents, not a certificate of completion. That score should update continuously and feed directly into what training or intervention someone gets next, not sit in a spreadsheet nobody opens again.
6. Extend the same model to AI agents, not just people
This is the part most legacy security awareness training doesn't cover at all: every AI agent in your organization is wielded by a person, and that agent's exposure is that person's exposure, executed automatically and at scale. An agent can be manipulated by a paragraph of untrusted text the same way a person can be manipulated by a convincing email.
The right response isn't to reach straight for governance policies and runtime blocks before you understand where the risk actually is. It's the same principle as everywhere else in this list: measure first. Map which people's agents are exposed based on their tools, their connected systems, and their behavior, then confirm with simulation which of those exposures an attacker could actually trigger. Controls without that measurement step are just friction, they slow everyone down and don't target the real risk.
7. Turn what you measure into targeted, ongoing coaching
None of the above works in isolation. Measurement without action is just a dashboard. The last piece is closing the loop: taking what continuous, multi-channel measurement tells you and turning it into coaching that's specific to the person and the risk, not a generic module sent to everyone regardless of exposure.
What this looks like: someone who fails a vishing simulation gets a short, targeted follow-up on voice-based social engineering, not a 40-minute refresher on phishing basics they already understand. This is what separates a Human Risk Management approach from security awareness training in the traditional sense: the response is proportional to the actual, current risk, not a fixed annual curriculum.
How Can Cimento Help?
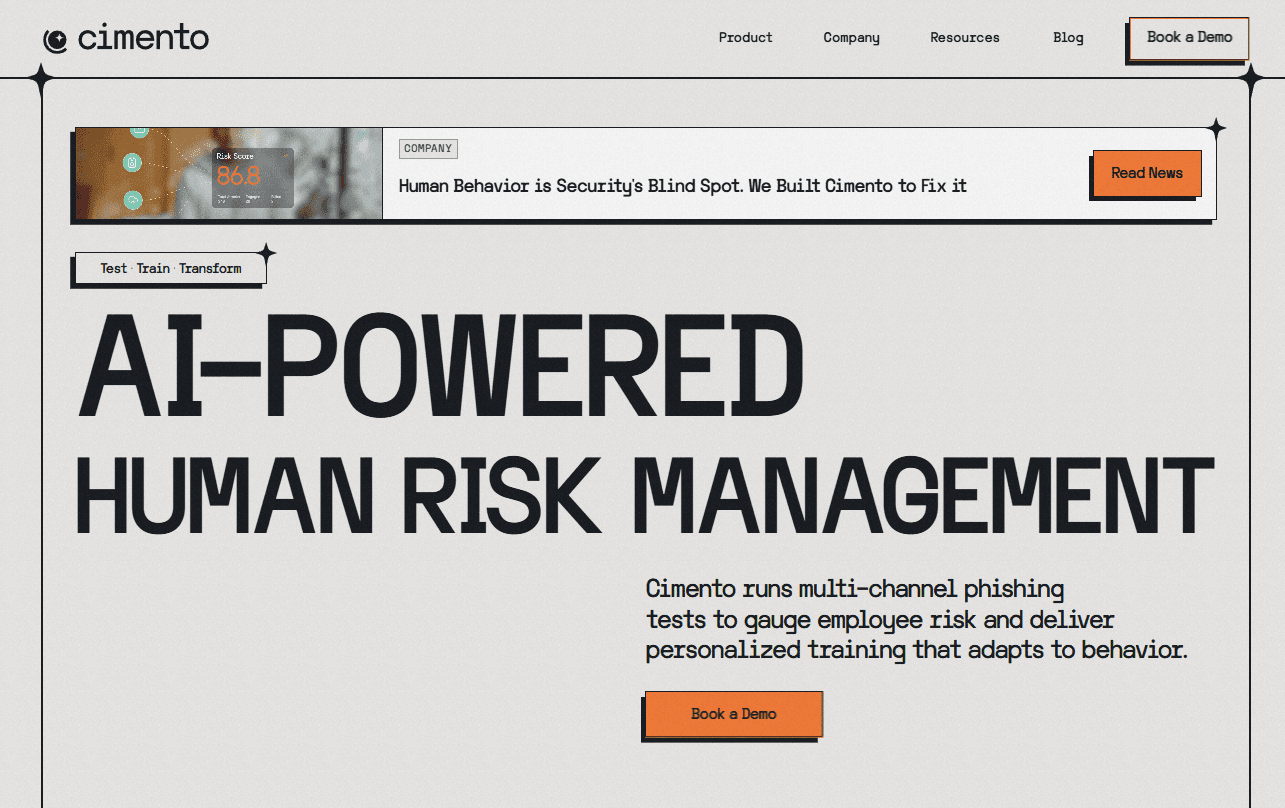
Everything above describes a shift from annual, compliance-driven training to continuous, behavior-based Human Risk Management. That shift is what Cimento is built around.
Cimento builds a living risk profile for every employee, not a static training record, by integrating with the tools people already use: email, identity providers, cloud services, and most of an organization's existing security stack. From there, the platform does three things continuously instead of annually:
Simulates realistic attacks across every channel, not just email. Cimento runs email, SMS, voice, and AI-enabled impersonation scenarios, often as multi-step sequences that unfold across multiple touchpoints rather than a single one-click test, mirroring how real attackers actually operate.
Scores risk continuously, by role. Instead of treating every employee the same, Cimento accounts for the fact that a developer with production access, a finance lead, and a new hire carry very different risk profiles, and scores exposure, behavior, and resilience accordingly.
Responds automatically. When risk is detected, Cimento delivers adaptive, in-the-moment coaching, typically 60 to 90 seconds, at the point of failure rather than queuing someone for a training module weeks later.
The same model extends to AI agents. As agents take on more enterprise access and workflows, they become a new, largely ungoverned attack surface, and Cimento treats agent exposure with the same measure-first approach it applies to people: map exposure, confirm it with simulation, then act.
If you want a starting point rather than a full rollout, Cimento offers a 14-day baseline that measures where your organization actually stands today, alongside whatever training or awareness program you're already running.
Parting Thoughts
Social engineering isn't going away, and it's not staying inside your inbox. The organizations that hold up aren't the ones with the longest training curriculum. They're the ones that know, in real time, where their actual exposure is, across every channel an attacker might use, and act on it before someone else finds the gap first.
See where your organization actually stands. Get your 14-day human risk baseline with Cimento.
FAQs About How to Prevent Social Engineering
1. What is a social engineering attack?
A social engineering attack is any attempt to manipulate a person, rather than a system, into handing over information or access. It relies on psychological pressure like urgency, authority, or trust instead of technical exploits, and it spans multiple channels: email, SMS, phone calls, and increasingly AI-generated deepfakes.
2. What's the difference between social engineering and phishing?
Phishing is one type of social engineering attack, specifically the kind delivered by email. Social engineering is the broader category that also includes smishing (SMS-based attacks), vishing (voice-based attacks), pretexting, and deepfake impersonation. Every phishing attack is social engineering, but not every social engineering attack is phishing.
3. What are the most common types of social engineering attacks?
The most common types are phishing (email), smishing (SMS), vishing (voice calls), pretexting (fabricated scenarios like a fake IT request), and increasingly, deepfake-driven impersonation using AI-generated audio or video.
4. How is preventing social engineering different from traditional security awareness training?
Traditional security awareness training measures whether someone completed a course. Preventing social engineering effectively means continuously measuring actual behavior and exposure, simulating the channels attackers really use, and adjusting coaching based on real risk rather than running the same annual module for everyone.
5. Can technology alone stop social engineering attacks?
No. Technical controls like MFA and email filtering raise the cost of an attack and catch a share of attempts, but social engineering is designed to bypass technology by targeting a person directly. The most effective defense pairs technical controls with continuous, behavior-based measurement and verification processes for high-risk requests.
Key Takeways
Replace annual training-only programs with continuous measurement of real employee behavior and exposure.
Simulate phishing, smishing, vishing, and deepfake attacks to test every channel attackers use.
Require independent verification for money transfers, credential resets, and other high-risk requests.
Pair human-layer defenses with strong technical controls such as MFA, access limits, and email authentication.
Turn observed risk into targeted, timely coaching instead of assigning the same training to everyone.


